Attack to Protect
Our comprehensive suite of offensive security services helps you identify vulnerabilities before attackers do. We think like adversaries to strengthen your defenses.
Web Application Penetration Testing
Comprehensive security assessment of your web applications following OWASP methodologies. We identify vulnerabilities such as SQL injection, XSS, authentication flaws, and business logic issues among others.
- OWASP Top 10 vulnerability assessment
- Authentication and session management testing
- API security testing (REST/GraphQL)
- Business logic flaw identification
- Comprehensive remediation guidance
External Penetration Testing
Simulate attacks from external threat actors to evaluate the security of your internet-facing infrastructure and identify potential entry points.
- Perimeter security assessment
- Service enumeration and vulnerability scanning
- Exploitation of identified weaknesses
- Social engineering vectors analysis
- Detailed risk prioritization
Internal Penetration Testing
Evaluate your internal network security from the perspective of an insider threat or compromised user to identify lateral movement opportunities.
- Active Directory security assessment
- Network segmentation testing
- Privilege escalation testing
- Credential harvesting simulation
- Data exfiltration analysis

Mobile Application Penetration Testing
Security assessment of iOS and Android applications including static and dynamic analysis to protect your mobile users and sensitive data.
- Static code analysis (SAST)
- Dynamic runtime analysis (DAST)
- API backend testing
- Data storage security review
- Transport layer security assessment
Cloud Security Testing
Evaluate the security posture of your cloud infrastructure across AWS, Azure, and GCP environments to identify misconfigurations and vulnerabilities.
- Cloud configuration review
- IAM policy assessment
- Container security testing
- Serverless function security
- Cloud-native vulnerability assessment
Red Team Operations
Full-scope adversary simulation that tests your organization's people, processes, and technology to evaluate detection and response capabilities.
- Advanced persistent threat simulation
- Physical security testing
- Social engineering campaigns
- Custom malware development
- Blue team exercises and debriefs
Source Code Review
Manual and automated review of your application source code to identify security vulnerabilities, coding flaws, and compliance issues.
- Manual code review by experts
- Automated SAST tool analysis
- Secure coding recommendations
- Framework-specific vulnerability detection
- Third-party library risk assessment
AI-Assisted Penetration Testing
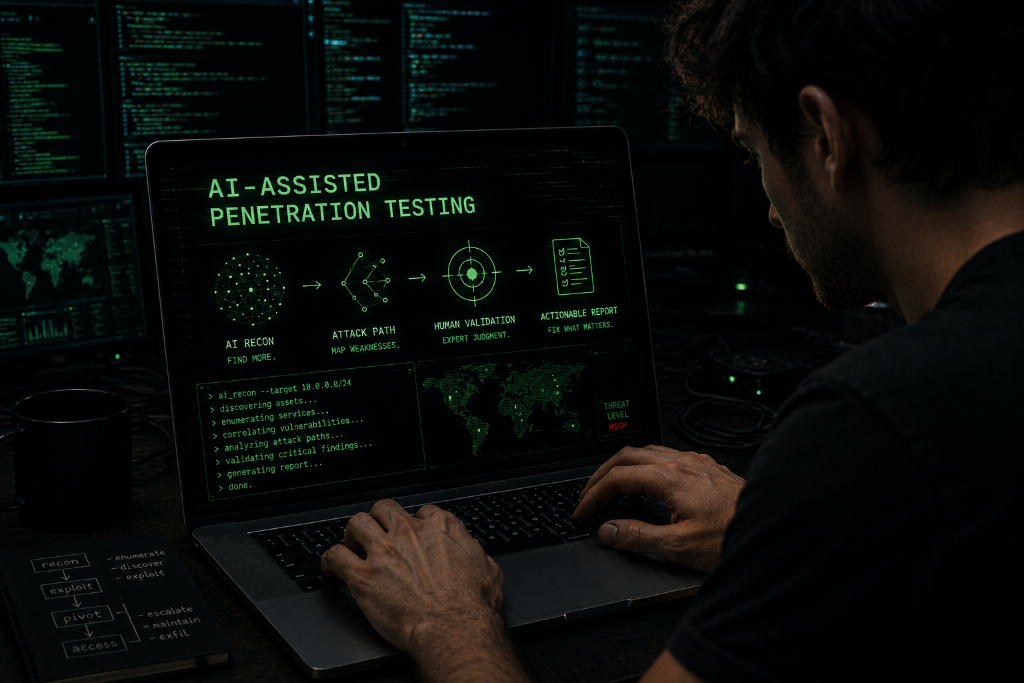
A new generation of security testing that fuses over two decades of real-world offensive security expertise with the power of artificial intelligence. Our AI-Assisted Penetration Testing service doesn't replace human judgment — it amplifies it. By running AI-driven reconnaissance, attack path analysis, and vulnerability correlation in parallel with our senior consultants, we achieve broader coverage in less time without sacrificing depth or accuracy.
- AI-driven attack surface discovery and enumeration
- Parallel vulnerability analysis across multiple attack vectors
- Human-validated findings — every critical issue reviewed by senior experts
- Faster turnaround without compromising testing depth
- Adaptive testing that evolves with your environment in real time
- Full narrative report with prioritized, actionable remediation steps
Vulnerability Assessment
Systematic identification and classification of security vulnerabilities in your infrastructure to prioritize remediation efforts.
- Network vulnerability scanning
- Asset discovery and inventory
- Vulnerability prioritization
- Compliance-focused assessments
- Ongoing monitoring recommendations
Need a Customized Security Assessment?
Our team will work with you to design a security testing program tailored to your specific needs and risk profile.
Contact Us Today